Compliance that feels like
having a security team
- Port St. Lucie
- Fort Pierce
- Stuart
- Palm City
- Jensen Beach
- Vero Beach
- Jupiter
- Palm Beach Gardens
One security lead. Risk assessment, policies, controls, evidence. A real security program is built this way. Yours is, too.
The program you own.
No portal you rent, no binder from a compliance vendor. Everything I build is yours, written for your firm, and stays with you if we ever part ways.
Risk analysis
Complete
Report delivered 2026-08-14
- Vendor BAA: cloud faxPending
- Laptop encryption: 2 devicesScheduled
- Q4 staff trainingNov 12
Fig. 2Sample client status · illustrative
Governance
- Named security lead of record
- Written, firm-specific risk assessment
- Annual report to ownership
Controls
- MFA everywhere it matters
- Encryption in transit and at rest
- Tested, offline backups
Evidence
- Policies mapped to the rule by section
- Vendor inventory and BAAs
- Audit-ready documentation
Response
- Written incident response plan
- 30-day notification clocks tracked
- A person to call at 7 a.m.
For years, a small regulated business had two options for security. Both required compromise.
Your IT provider
Support, but not a program
- Patches and helpdesk, not risk assessments and policies
- Nobody named as the Qualified Individual or security lead
- Compliance as one bullet inside a managed-IT bundle
- Finger-pointing when the auditor or insurer shows up
A national compliance firm
Expertise, but at a cost
- An account manager between you and whoever does the work
- Retainers priced for 500-person companies
- Templates with your firm name pasted in
- Nobody who will drive to your office
For the first time, real security leadership fits a 12-person practice.
One named security lead
A CISSP-certified person who builds your program, runs it, and answers when you call. No account manager, no rotating consultants.
Learn more →Predictable, published costs
Anchor prices on the site for every package. No hourly surprises, no "call for pricing," and a baseline assessment credited toward whatever you start.
Learn more →Rule-driven deliverables
Everything maps to a section number: 16 CFR 314, 45 CFR 164, NIST SP 800-171. Your auditor, insurer, or prime can trace every control.
Learn more →20-minute setup
One call. Then a two-week baseline. Then a program that runs on a quarterly or monthly cadence with a phone that gets answered.
Learn more →The biggest gap in small-business security is that nobody owns it.
Every control on your program has a section of the rule it satisfies, a named owner, and a date. That is the whole difference between "we have security" and being able to prove it.
| Name | Requirement | Owner | State | Updated |
|---|---|---|---|---|
| risk-analysis | HIPAA 164.308(a)(1) | Ed | complete | 3w |
| wisp-v2 | FTC 314.4(b) | Ed | complete | 2mo |
| mfa-rollout | FTC 314.4(c)(5) | MSP | complete | 1mo |
| backup-restore-test | NIST 800-171 3.8.9 | MSP | scheduled | 4d |
| vendor-baas | HIPAA 164.308(b) | Office mgr | in progress | 1w |
| ir-plan | FTC 314.4(h) | Ed | complete | 1mo |
| staff-training-q4 | FTC 314.4(e) | Ed | scheduled | 12d |
| insurance-questionnaire | Carrier renewal | Ed | submitted | 2w |
| sprs-affirmation | DFARS 7019 | Owner | in progress | 5d |
| annual-report | FTC 314.4(i) | Ed | scheduled | 2mo |
Get compliance updates and Treasure Coast security news
Purpose-built for regulated small businesses
Tax preparers & CPAs →
FTC Safeguards Rule and IRS Publication 4557. A WISP built for your firm and a named Qualified Individual on retainer.
WISP Build · $3,500 one-time
Medical & dental practices →
A HIPAA Security Rule risk analysis OCR would accept, policies staff will follow, and BAAs on every vendor.
Essentials · from $2,500 /month
RIAs & wealth managers →
Regulation S-P incident response program, service-provider oversight, and the 30-day notification process, in force since June 2026.
Defense & aerospace suppliers →
Level 1 self-assessments done right, honest SPRS scores, and Level 2 readiness with an SSP and POA&M a C3PAO will accept.
Level 1 Self-Assessment Package · $4,500 one-time
Law firms & title companies →
Client-confidentiality and wire-fraud controls, plus the security program your malpractice and cyber carriers now ask about.
Cyber-insurance renewals →
The questionnaire completed and defended by someone who understands the controls, so a claim is never denied for a misstatement.
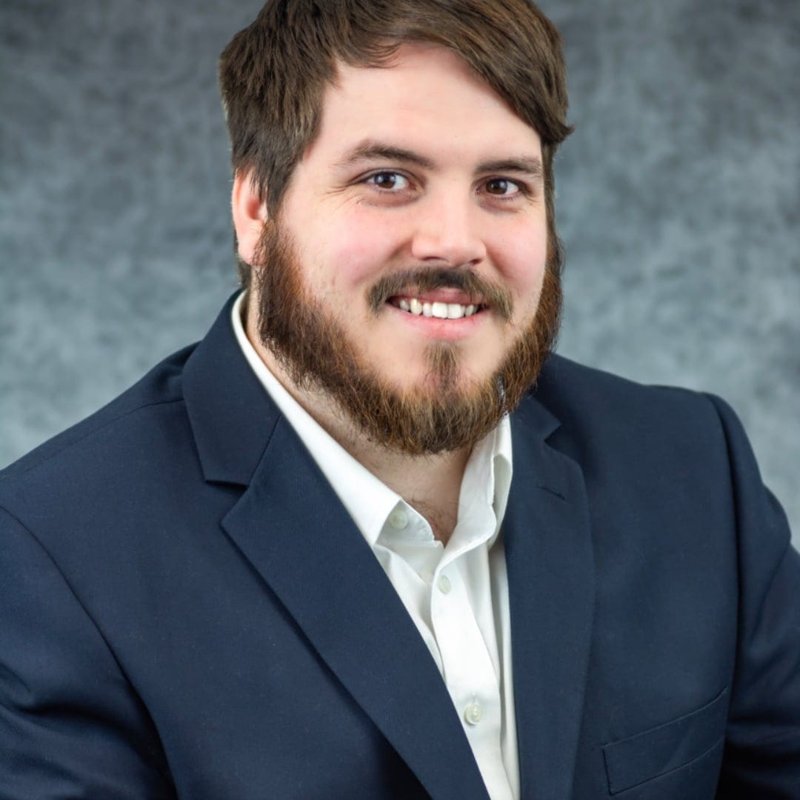
The person on your program is the person you talk to.
Larger firms put an account manager between you and whoever does the work. Here there is one of me, and you will always know who is responsible for your program.
- 1
CISSP certified
The senior security certification issued by ISC2, and the one regulated buyers look for. You can confirm it with the link below.
- 2
Ten-plus years in the work
Offensive security, cloud security, and building security programs from zero in regulated healthcare environments. I know what attackers do, what auditors ask for, and what small businesses skip.
- 3
Port St. Lucie, on-site
I know which primes send flow-down letters here, which carriers are tightening renewals, and which local IT providers are good. I will show up.
One person. One number. One program that runs the same way every time.
- ✓Works with your existing MSP, Microsoft 365, EHR, and tax software
- ✓Evidence collected as we go, so audit day is a formality
- ✓Everything you receive is yours to keep
Assess
A 20-minute call, then a two-week baseline assessment. Written findings, a ranked fix list, and a straight answer on what you need. If the answer is "not much," you will hear it.
Build
Risk assessment, written plan, policies, incident response, and a short fix list with owners and dates. I coordinate the technical work with the IT provider you already have.
Run
I stay on as your named security lead: Qualified Individual, vCISO, or compliance owner. Quarterly or monthly cadence, annual reporting, exam support, and a phone that gets answered.
Grandmas are free.
If you are a grandma on the Treasure Coast and your computer, phone, or email is giving you trouble, I will fix it for free. House call if you are close. No proof required. In honor of my grandma Agnes.
Free senior cyber-safety talks for libraries, churches, HOAs, and senior centers, too.